The mortgage servicing technology provider has secured its SOC 2 Type II attestation for the fourth year running after KPMG tested 89 controls over twelve months

Mortgage and savings technology provider Phoebus Software has passed its SOC 2 Type II attestation for the fourth year running. KPMG conducted the independent assessment across the twelve months to 31 July 2026.
The Service Organisation Control 2 (SOC 2) Type II standard is developed by the American Institute of Certified Public Accountants (AICPA). It requires firms to show that information security controls are fit for purpose. More importantly, it verifies that those controls are operating consistently in practice, not just on paper.
That distinction carries real weight for UK mortgage professionals who rely on third-party servicing platforms. A provider holding SOC 2 Type II assurance has been independently verified to manage client data with consistent rigour across an extended operational window.
The 2026 assessment tested 89 unique controls across Phoebus's systems. KPMG identified only two minor exceptions during the reporting period. The company first secured the attestation in 2023. Each subsequent assessment has returned a cleaner result.
Why do mortgage technology security assessments matter for lenders and brokers?
For lenders and brokers assessing technology partners, independent attestations provide auditor-verified evidence – something that carries far more weight than a self-reported policy.
The Financial Conduct Authority (FCA) expects firms to manage operational risk across their supply chains. When a technology provider services mortgage accounts on a lender's behalf, the data protection posture of that platform becomes the lender's responsibility too.
As more mortgage platforms seek recognised certifications – from CRM providers obtaining ISO 27001 accreditation to specialist servicing firms landing major new contracts – independent assurance is becoming a standard expectation rather than an optional extra.
Dale Langham, information security officer at Phoebus Software in Solihull, said the independent nature of the assessment was central to its value for clients. "This independent assessment provides our current and prospective clients with significant assurance that Phoebus continues to maintain robust controls aligned with recognised industry standards and best practice," he said.
He added that the result also strengthened Phoebus's capacity to support client due diligence and supplier assurance processes. It also reflected a broader commitment to risk management and operational consistency across the business.
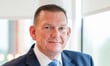
Richard Pike (pictured above), chief sales and marketing officer at Phoebus Software, said the consecutive track record was a meaningful signal for organisations evaluating the platform. The latest result sits alongside Phoebus's ISO/IEC 27001:2022 certification, which covers information security management under a separate international standard.
"SOC 2 Type II attestation is increasingly recognised across the financial services sector as an important demonstration of effective control practices," Pike said. "Achieving this for the fourth consecutive year, alongside our ISO/IEC 27001:2022 certification, provides prospective and existing clients with confidence that information security, risk management, and operational excellence remain at the heart of our business."
A market-wide push for verified credentials
The result arrives as independent data credentialing becomes more prominent across UK mortgage technology. CRM and origination platforms have moved in numbers to obtain recognised certifications driven by client pressure and stricter regulatory expectations around data handling.
Founded in 1989 and now operating across more than 25 organisations in the UK and Ireland, Phoebus manages over £120 billion in assets on its platform. Maintaining the SOC 2 standard requires consistent policy adherence across the entire workforce. Pike noted that the 2026 result reflects a business-wide commitment rather than a siloed compliance exercise.
The SOC 2 Type II attestation provides documented, third-party confirmation that its controls held to standard across a full year of live operations. As regulatory scrutiny of third-party technology providers intensifies, that independently verified track record is increasingly what due diligence demands.