Deepfakes and synthetic identities put client verification under scrutiny

Financial firms in New Zealand should assume cyber incidents linked to frontier artificial intelligence (AI) will happen, and boards must take clear ownership of the risk. That is the message from the Reserve Bank (RBNZ) and the Financial Markets Authority (FMA).
The two regulators set out their supervisory expectations on cyber risk associated with frontier AI at an Auckland roundtable, co-hosted with the Department of the Prime Minister and Cabinet and the National Cyber Security Centre (NCSC).
The expectations build on existing prudential, conduct, and operational resilience obligations. They focus on three pressure points: sharper cyber threats, governance settings being tested, and growing dependence on a handful of AI and cloud providers.
Fraud and verification in the spotlight
Alongside those three areas, the regulators flagged a fourth with direct consumer impact: AI-enabled fraud. They named deepfake impersonation, synthetic identities, and more convincing social engineering as threats, and asked firms to check whether their customer and employee verification processes still hold up.
They also told entities to assume incidents will occur and prepare for them. That means maintaining response and recovery protocols and stress-testing them against scenarios such as high-speed attacks, model failures, and supplier outages.
The FMA is also examining the issue from the advice side, through a thematic review of AI in financial advice. The review looks at how advice providers use AI tools and what that means for consumer outcomes.
Boards carry the accountability
Both regulators stressed that oversight has to keep pace with how quickly the technology is being adopted, a theme that echoes the FMA’s earlier research on AI adoption across financial services.
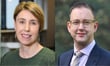
FMA executive director of response and enforcement Louise Unger (pictured left) said accountability starts at the top:
“Boards and senior management need to know where AI is being used in their business, understand the risks it brings, and be clear about who is accountable for managing them,” Unger said.
Suppliers and legacy systems
Because the sector relies heavily on a small number of AI and cloud providers, a problem at one provider could ripple across the sector. Outsourcing does not shift responsibility: accountability for operational risk stays with the regulated entity.
Firms running out-of-support legacy systems were told their exposure is growing, because frontier AI shortens the gap between a vulnerability being found and being exploited. The regulators called for faster, risk-based patching, while managing the risks that speed brings, alongside strong basic controls such as identity and access management.
RBNZ assistant governor for financial stability Angus McGregor (pictured right) summed up the regulators’ position:
“The core message today is simple: advances in AI are changing the operating environment for financial institutions,” McGregor said. “Entities are responsible for ensuring that they have the systems and controls in place to manage the risks arising from AI.”
Stay informed with the latest housing market trends and mortgage insights — subscribe to our free daily newsletter.